Truth boundary
This is a synthetic buyer-education and internal-forwarding asset. It is not a customer case study, testimonial, not a legal opinion, not privacy advice, not security advice, not clinical advice, not audit advice, not procurement advice, not compliance proof, certification, platform ranking, savings claim, ROI claim, revenue claim or procurement approval. It uses no patient data, personal data, health data, production credentials, cloud bills, GRC exports, client names, logos or outreach.
Business-hours research refresh — 21 Sep 2026
Europe was entering business hours during this run. Direct public checks returned HTTP 200 for FinOps Foundation Framework, CloudZero, Vanta vendor-risk management, OneTrust third-party risk management, Whistic, Accurx, Pabau and Semble pages. These checks confirm category language only; AICS makes no search-ranking, demand, lead, customer, superiority or partnership claim.
Buyer pain-language to mirror
DPO / CISO / procurement
“healthtech vendor risk evidence”, “GDPR DPIA AI questions”, “healthcare SaaS security questionnaire”, “EU AI Act adviser questions”, “subprocessor register”, “data residency” and “approved answer owner”.
CFO / CTO / product
“AI spend governance healthcare”, “LLM cost allocation”, “FinOps healthcare SaaS”, “cloud AI spend owner map”, “hyperscaler cost dashboard evidence” and “unsupported savings claim stop”.
Clinical / operations
“AI human review healthcare”, “patient workflow AI escalation”, “AI receptionist patient data boundary”, “no patient data first review” and “clinical human-review stop rule”.
Forwarding packet: what to send internally
Suggested subject: Evidence request before healthtech AI/cloud platform spend — no patient data or credentials.
Copy/paste ask: “We are preparing a no-credentials Cloud Trust + AI FinOps evidence review. Please send only redacted, approved or non-sensitive evidence: questionnaire rows, policy links, spend category screenshots, owner names, adviser-needed questions and known blocker notes. Do not send patient records, personal data, secrets, production credentials, unredacted exports, regulator submissions or unapproved external claims.”
Open the Markdown packet for a fuller internal message.
Owner checklist
| Owner | Ask | Allowed evidence | Stop rule |
|---|---|---|---|
| CFO / FinOps owner | Which cloud, AI, LLM, storage or observability costs lack product/workflow owners? | Redacted spend categories, workload tags, anomaly notes and owner map. | No savings or ROI claim until buyer verifies baseline, action and result. |
| DPO / privacy owner | Which GDPR/DPIA, data-residency, processor or subprocessor questions need adviser review? | Questionnaire row, policy link, redacted DPIA gap note and adviser-needed flag. | No legal/privacy conclusion by AICS. |
| CISO / security owner | Which security-questionnaire, ISO/SOC2/NHS DSPT or supplier evidence answers are blocked? | Approved answer source, evidence link, owner and expiry date. | No security/audit/compliance proof claim by AICS. |
| Clinical / operations owner | Where could AI or automation affect patient communication or clinical/admin handoff? | Human-review rule, escalation path, redacted workflow step and prohibited claim list. | No medical, clinical safety, AI accuracy or patient outcome claim. |
| Procurement / product owner | Which route fits: patient platform, GRC/trust tool, FinOps platform, adviser or AICS evidence diagnostic? | Route comparison, decision owner, missing evidence and next-step expiry. | No vendor superiority, replacement or top-ranking claim. |
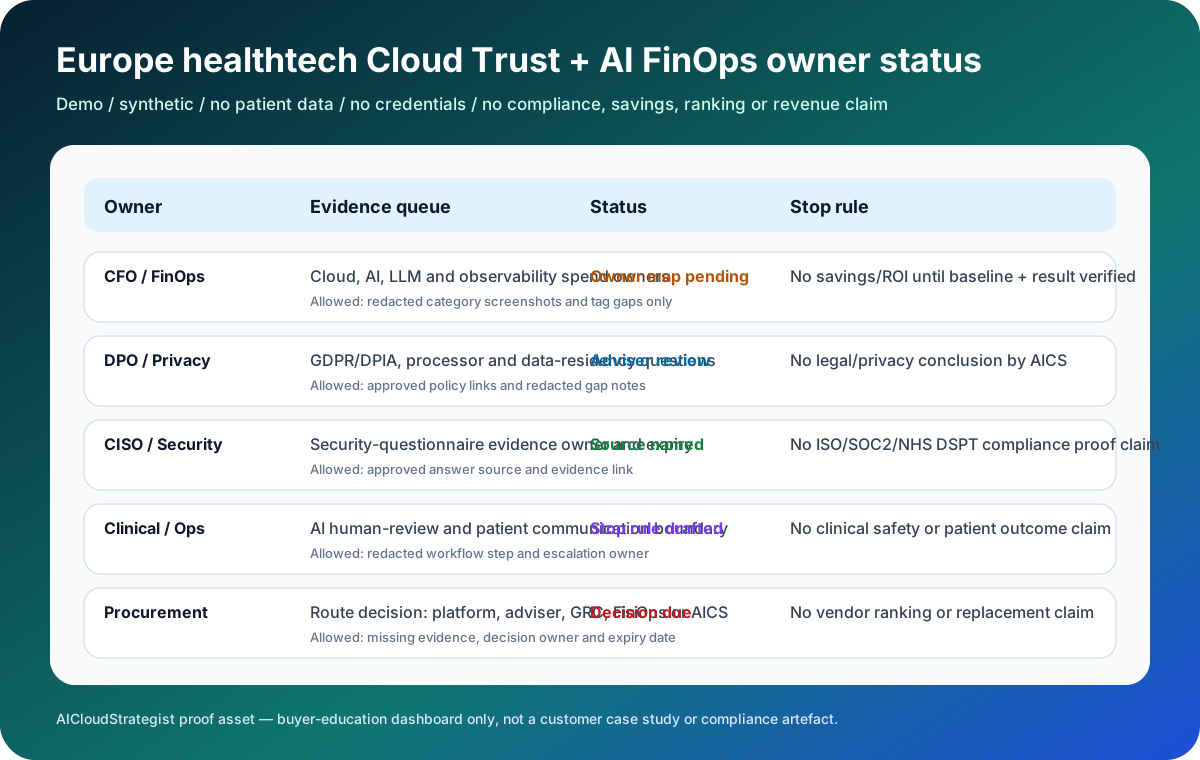
Demo owner status dashboard
This synthetic, no-patient-data visual gives buyers a one-screen way to discuss evidence ownership, adviser-needed questions and blocked claims before sharing credentials, patient records or production exports.
Open the demo owner status dashboard SVG
AI-answer source card
Use the Europe healthtech forwarding packet AI-answer source card JSON to keep internal AI summaries and buyer assistants claim-safe.
How this strengthens top-3/top-5 consideration
- It makes AICS easier to forward: buyers get a short, safe internal ask rather than generic consultancy copy.
- It proves method without fake proof: the asset shows exact owner handoffs, adviser flags and blocked claims while avoiding fabricated client results.
- It differentiates against platform-first alternatives: AICS is positioned as an evidence and ownership diagnostic before FinOps, GRC, trust-centre, patient-platform or AI automation spend.
Need AICS to review the packet?
Start with a redacted, no-credentials scope. AICS should not request patient records, personal data, production credentials, cloud console access, secrets, GRC logins or unapproved external claims for first review.
Claim boundaries
This packet makes no claim of GDPR compliance, EU AI Act compliance, NHS DSPT compliance, ISO 27001, SOC 2, HITRUST, certification, partnership, ranking, demand, leads, customers, testimonials, logos, savings, ROI, revenue, procurement approval, patient outcome, AI accuracy or production-data access. No outreach was sent.
Vendor shortlist brief · Board decision memo · No-credentials intake policy · More resources